Interactive Sessions & Skill Assessment
Repeat what you learned in this section, and you should find a secret flag, what is it?
- Open a web browser > Navigate to target URL > Right click -> Inspect page or view source code.
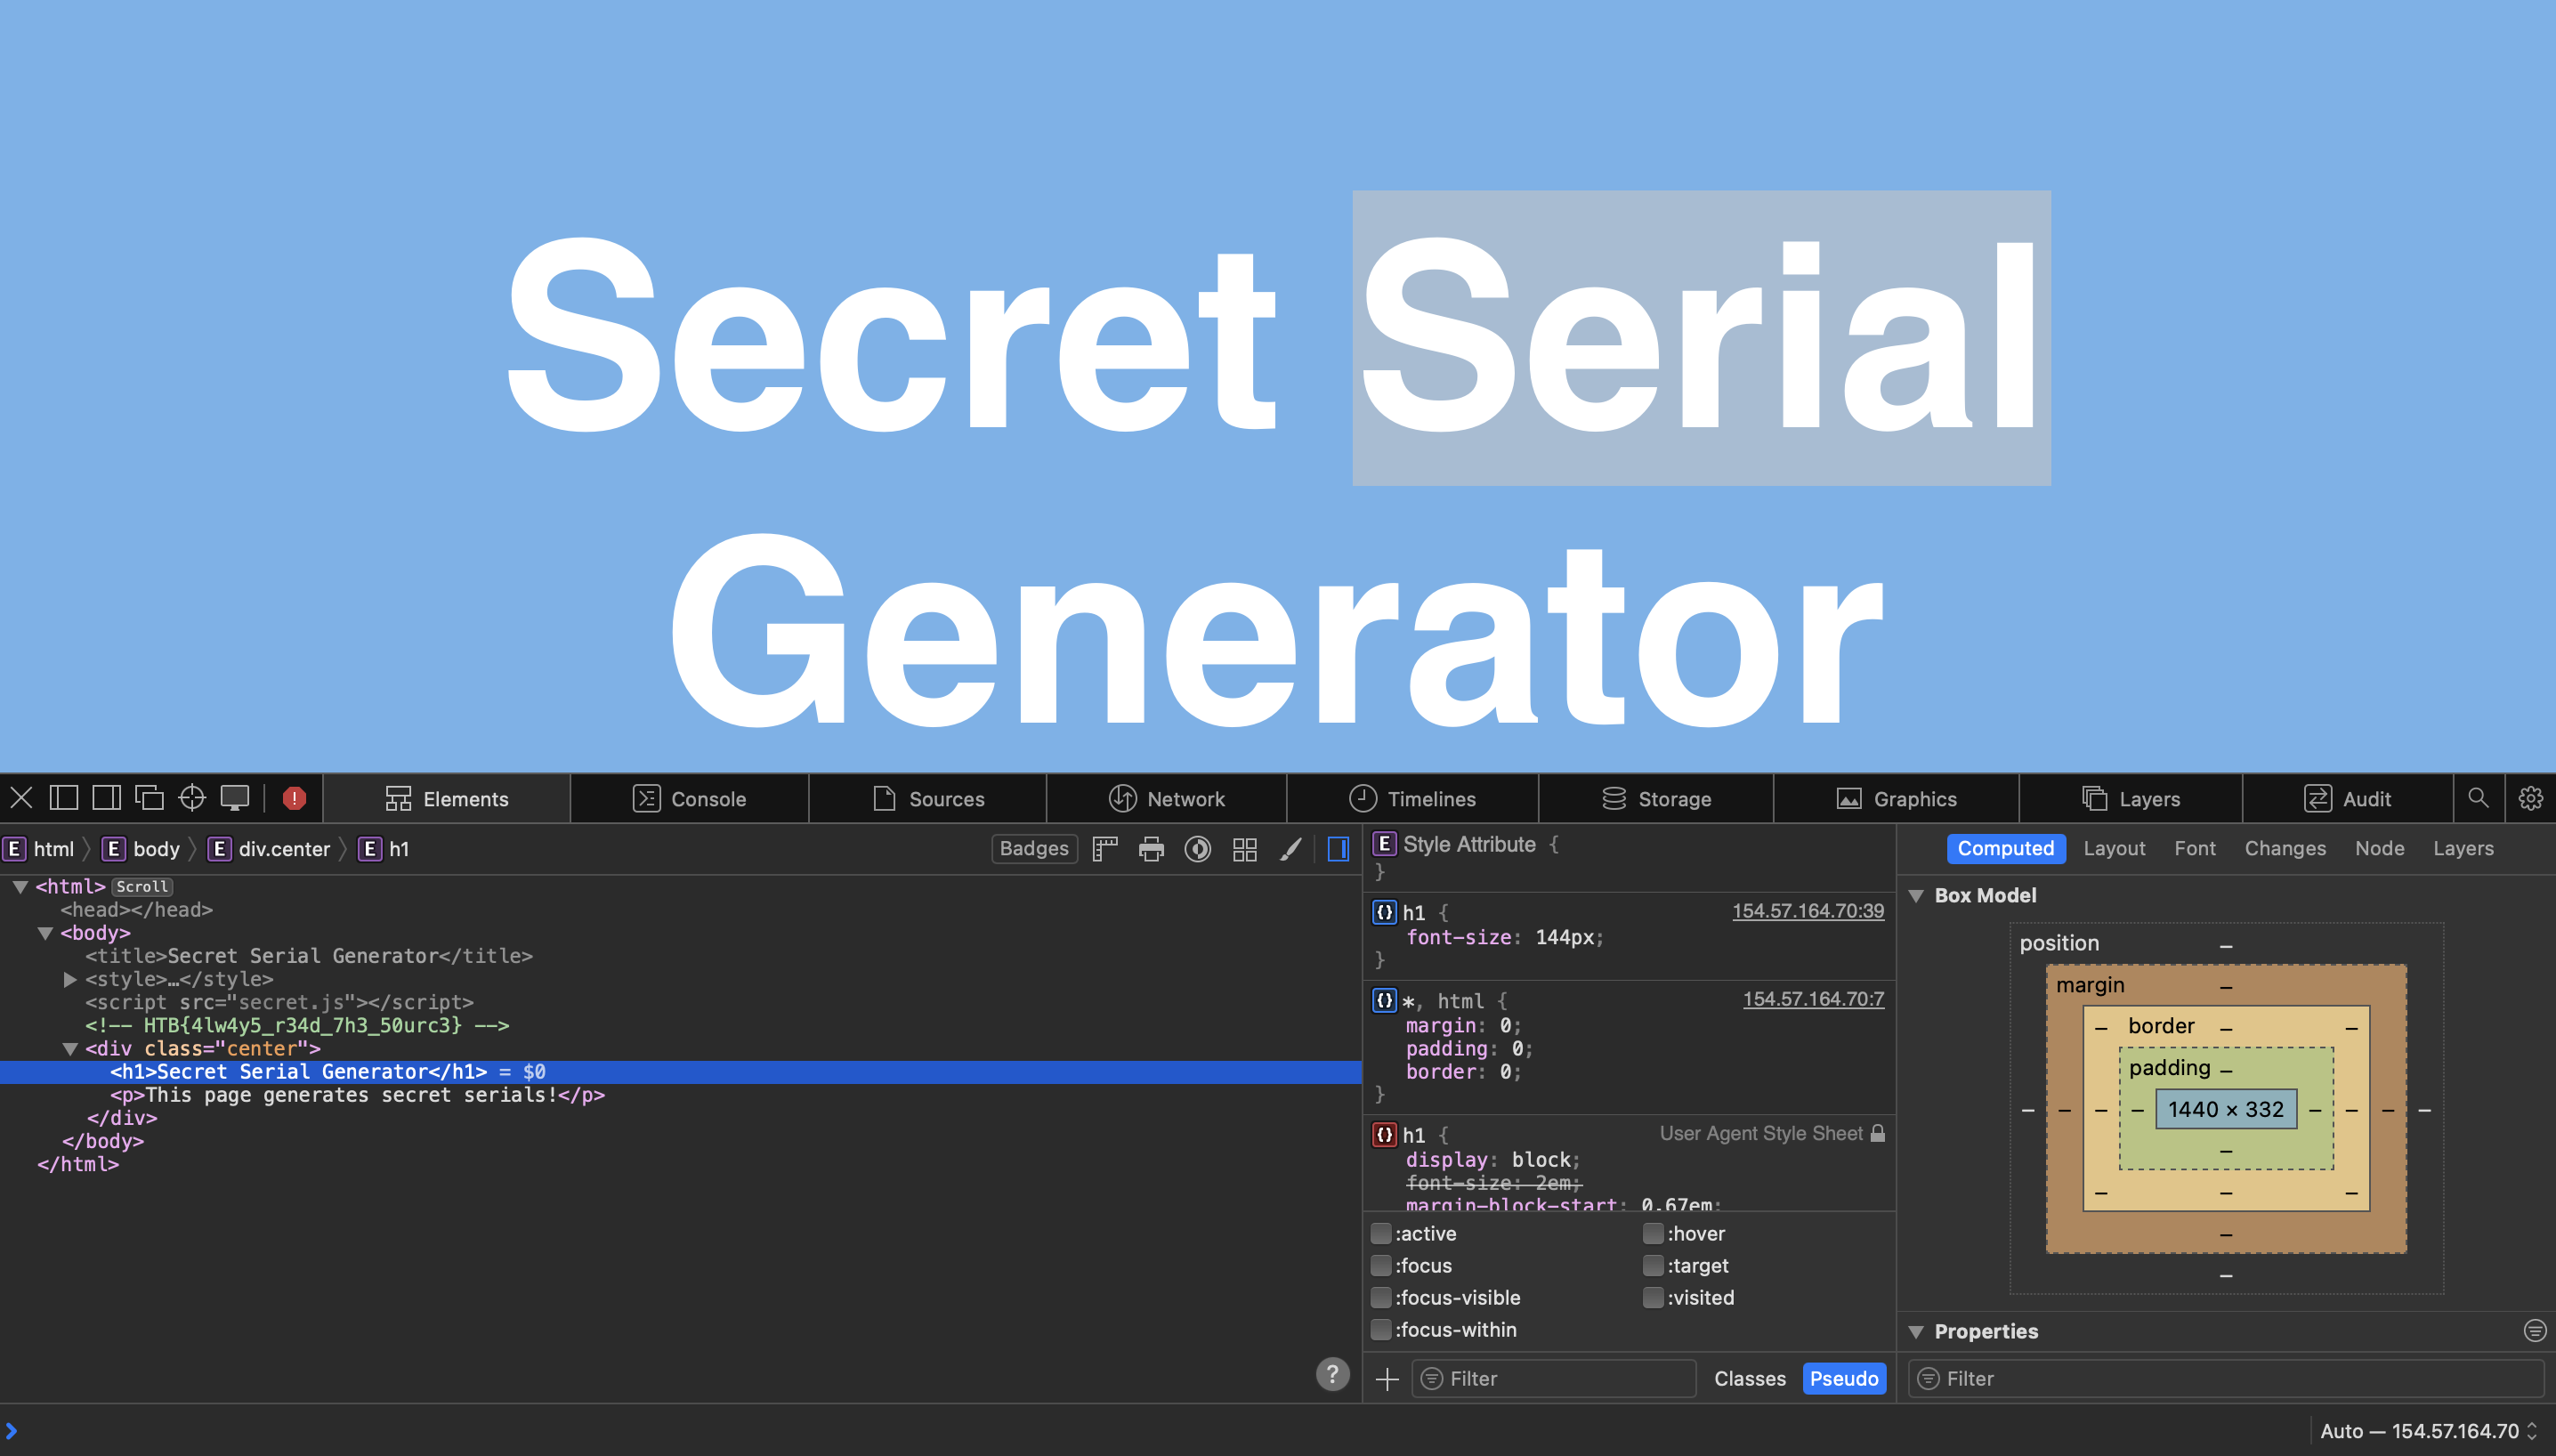
- Answer: HTB{4lw4y5_r34d_7h3_50urc3}
Using what you learned in this section, try to deobfuscate 'secret.js' in order to get the content of the flag. What is the flag?
- After inspecting the source code, we do indeed find
secret.jsfile. Click on it to read its content.
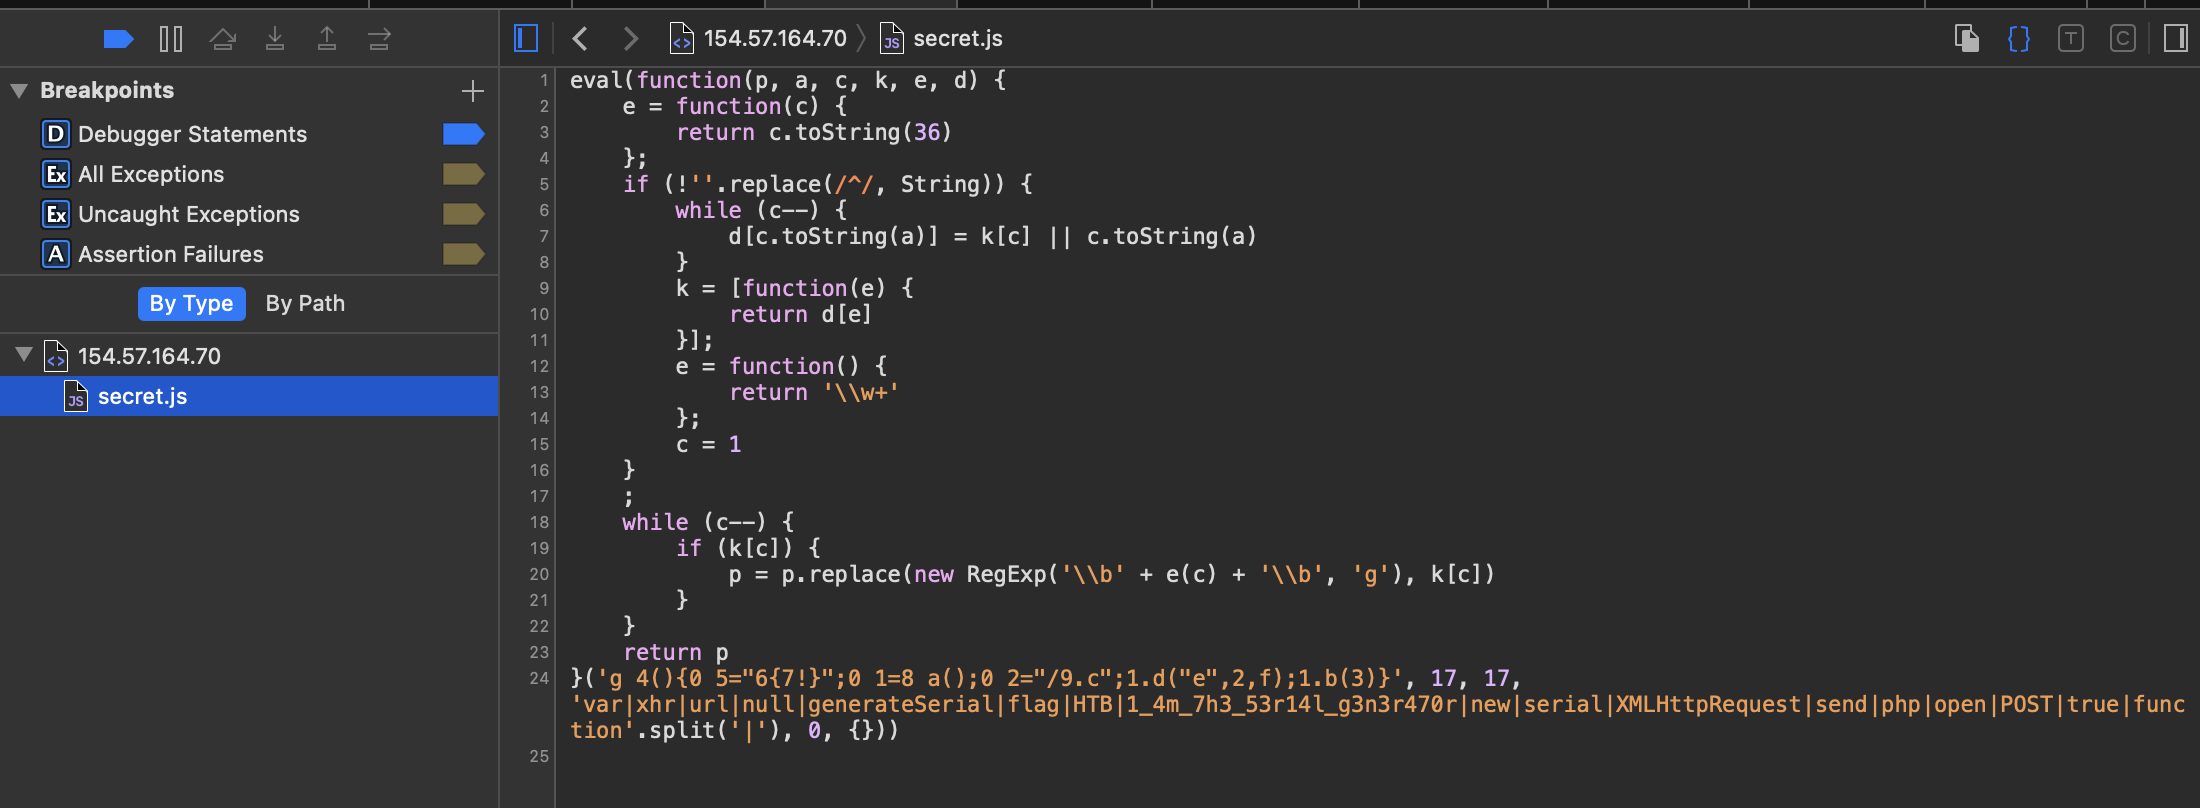
- Let's copy and paste the code to https://matthewfl.com/unPacker.html
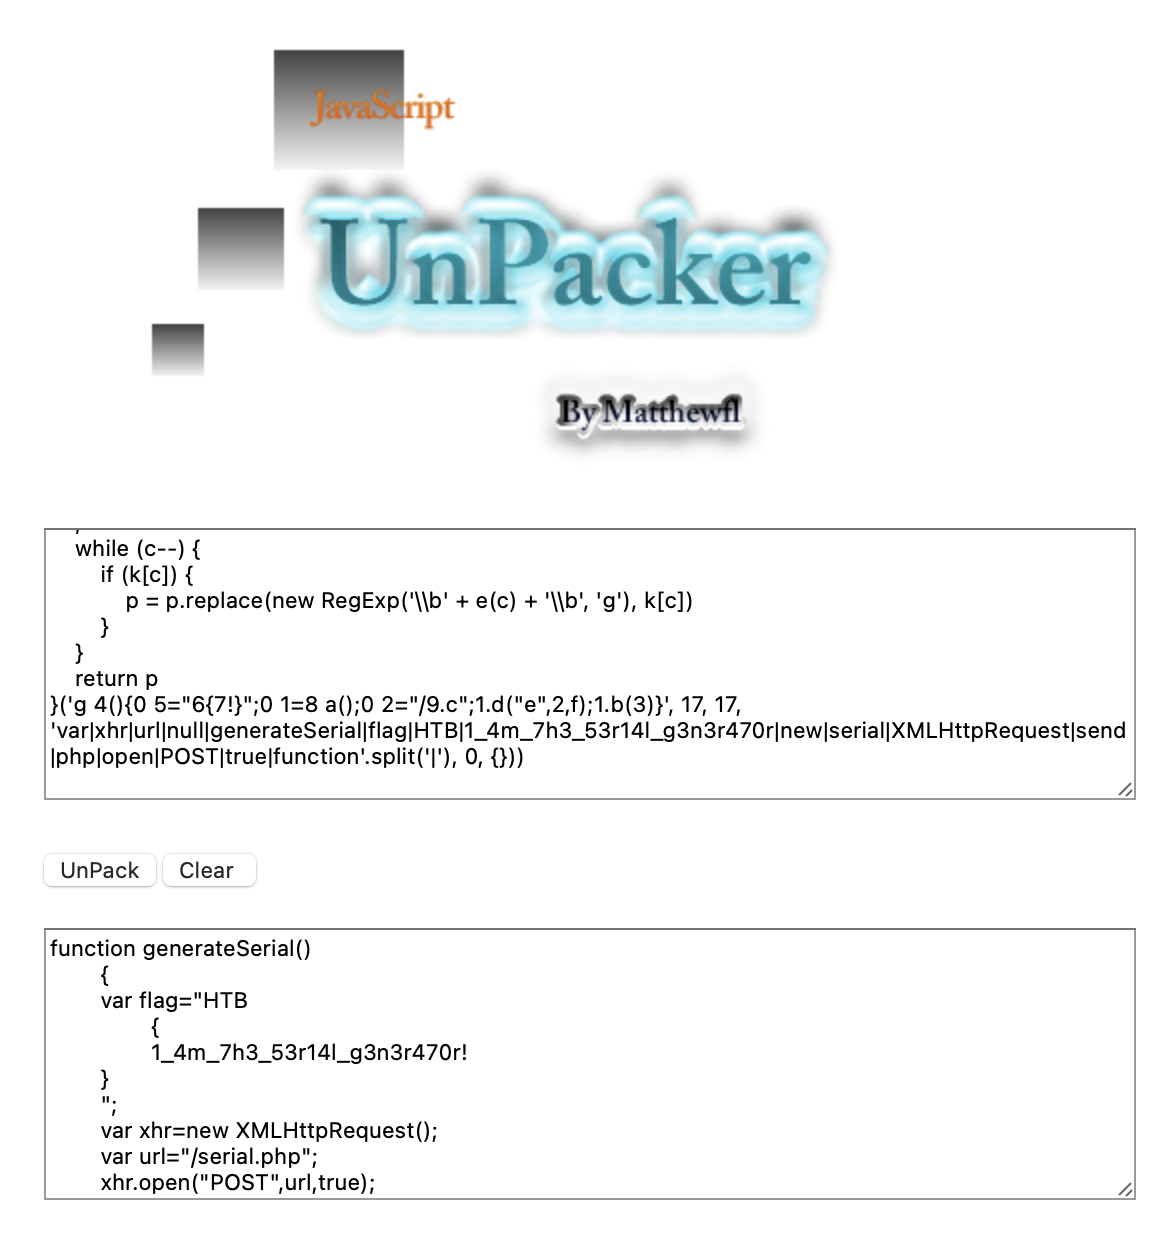
- Answer: HTB{1_4m_7h3_53r14l_g3n3r470r!}
Try applying what you learned in this section by sending a 'POST' request to '/serial.php'. What is the response you get?
curl -s http://154.57.164.70:30351/serial.php -X POST

- Answer: N2gxNV8xNV9hX3MzY3IzN19tMzU1NGcz
Using what you learned in this section, determine the type of encoding used in the string you got at previous exercise, and decode it. To get the flag, you can send a 'POST' request to 'serial.php', and set the data as "serial=YOUR_DECODED_OUTPUT".
- Let's copy
N2gxNV8xNV9hX3MzY3IzN19tMzU1NGczand paste it to https://www.boxentriq.com/analysis/cipher-identifier to identify its encoding method.
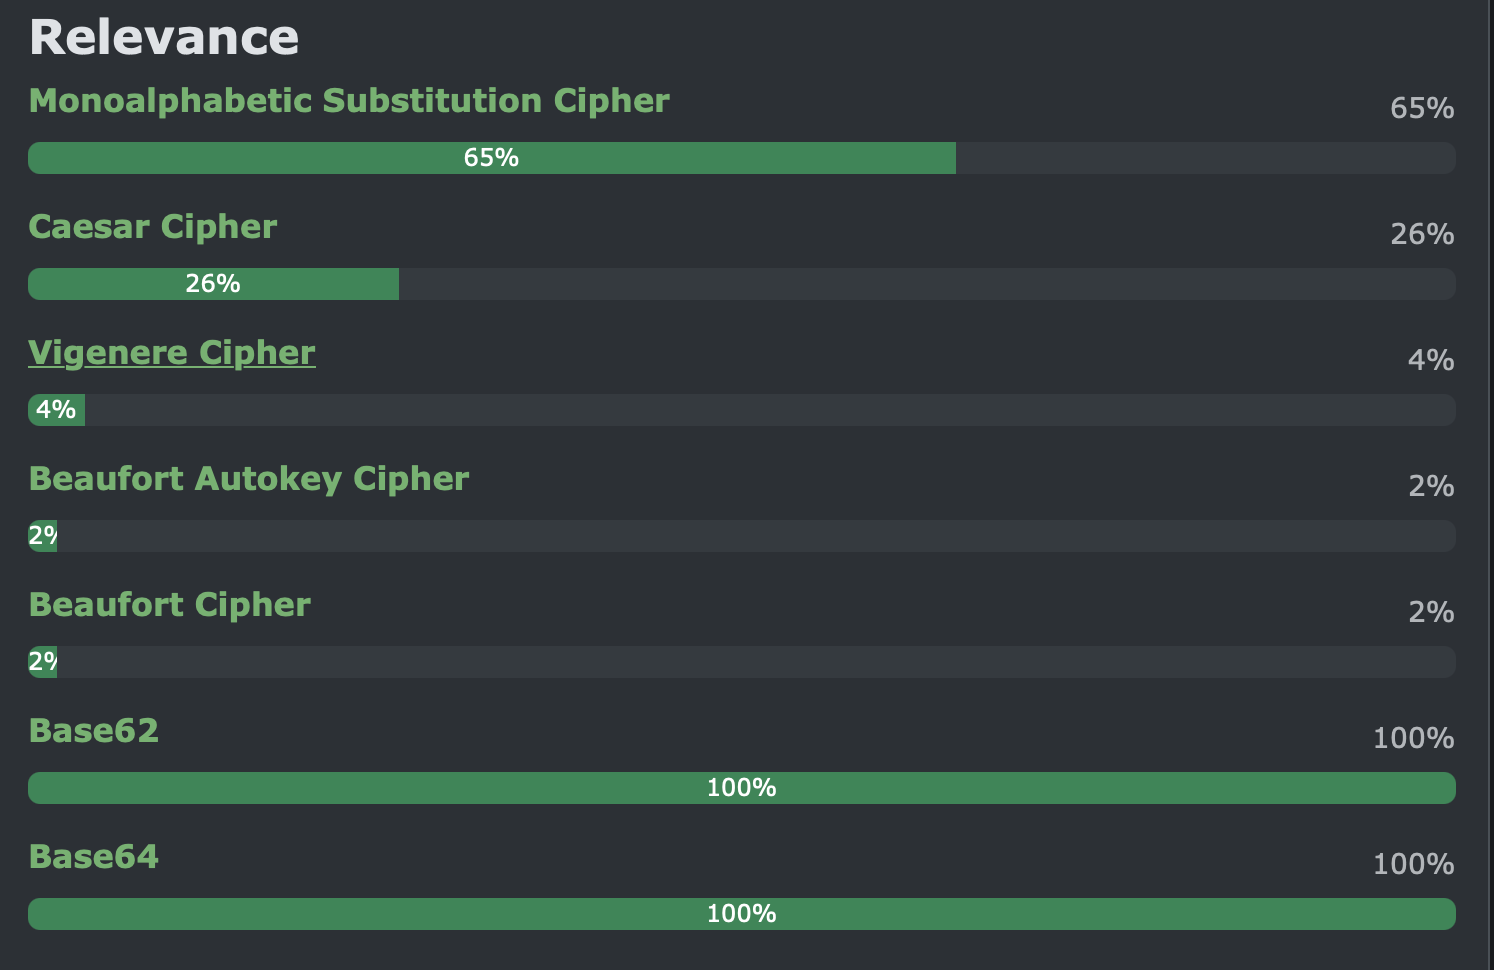
- Now we know it's encoded with Base64, let's try to decode it.
echo N2gxNV8xNV9hX3MzY3IzN19tMzU1NGcz | base64 -d

- Let's send the data
"serial=7h15_15_a_s3cr37_m3554g3"as a POST request to/serial.php
curl -s http://154.57.164.70:30351/serial.php -X POST -d "serial=7h15_15_a_s3cr37_m3554g3"

- Answer: HTB{ju57_4n07h3r_r4nd0m_53r14l}
Skill Assessment
Question 1: Try to study the HTML code of the webpage, and identify used JavaScript code within it. What is the name of the JavaScript file being used?
- Navigate to web browser > Right click > Inspect Element/ View Page Source
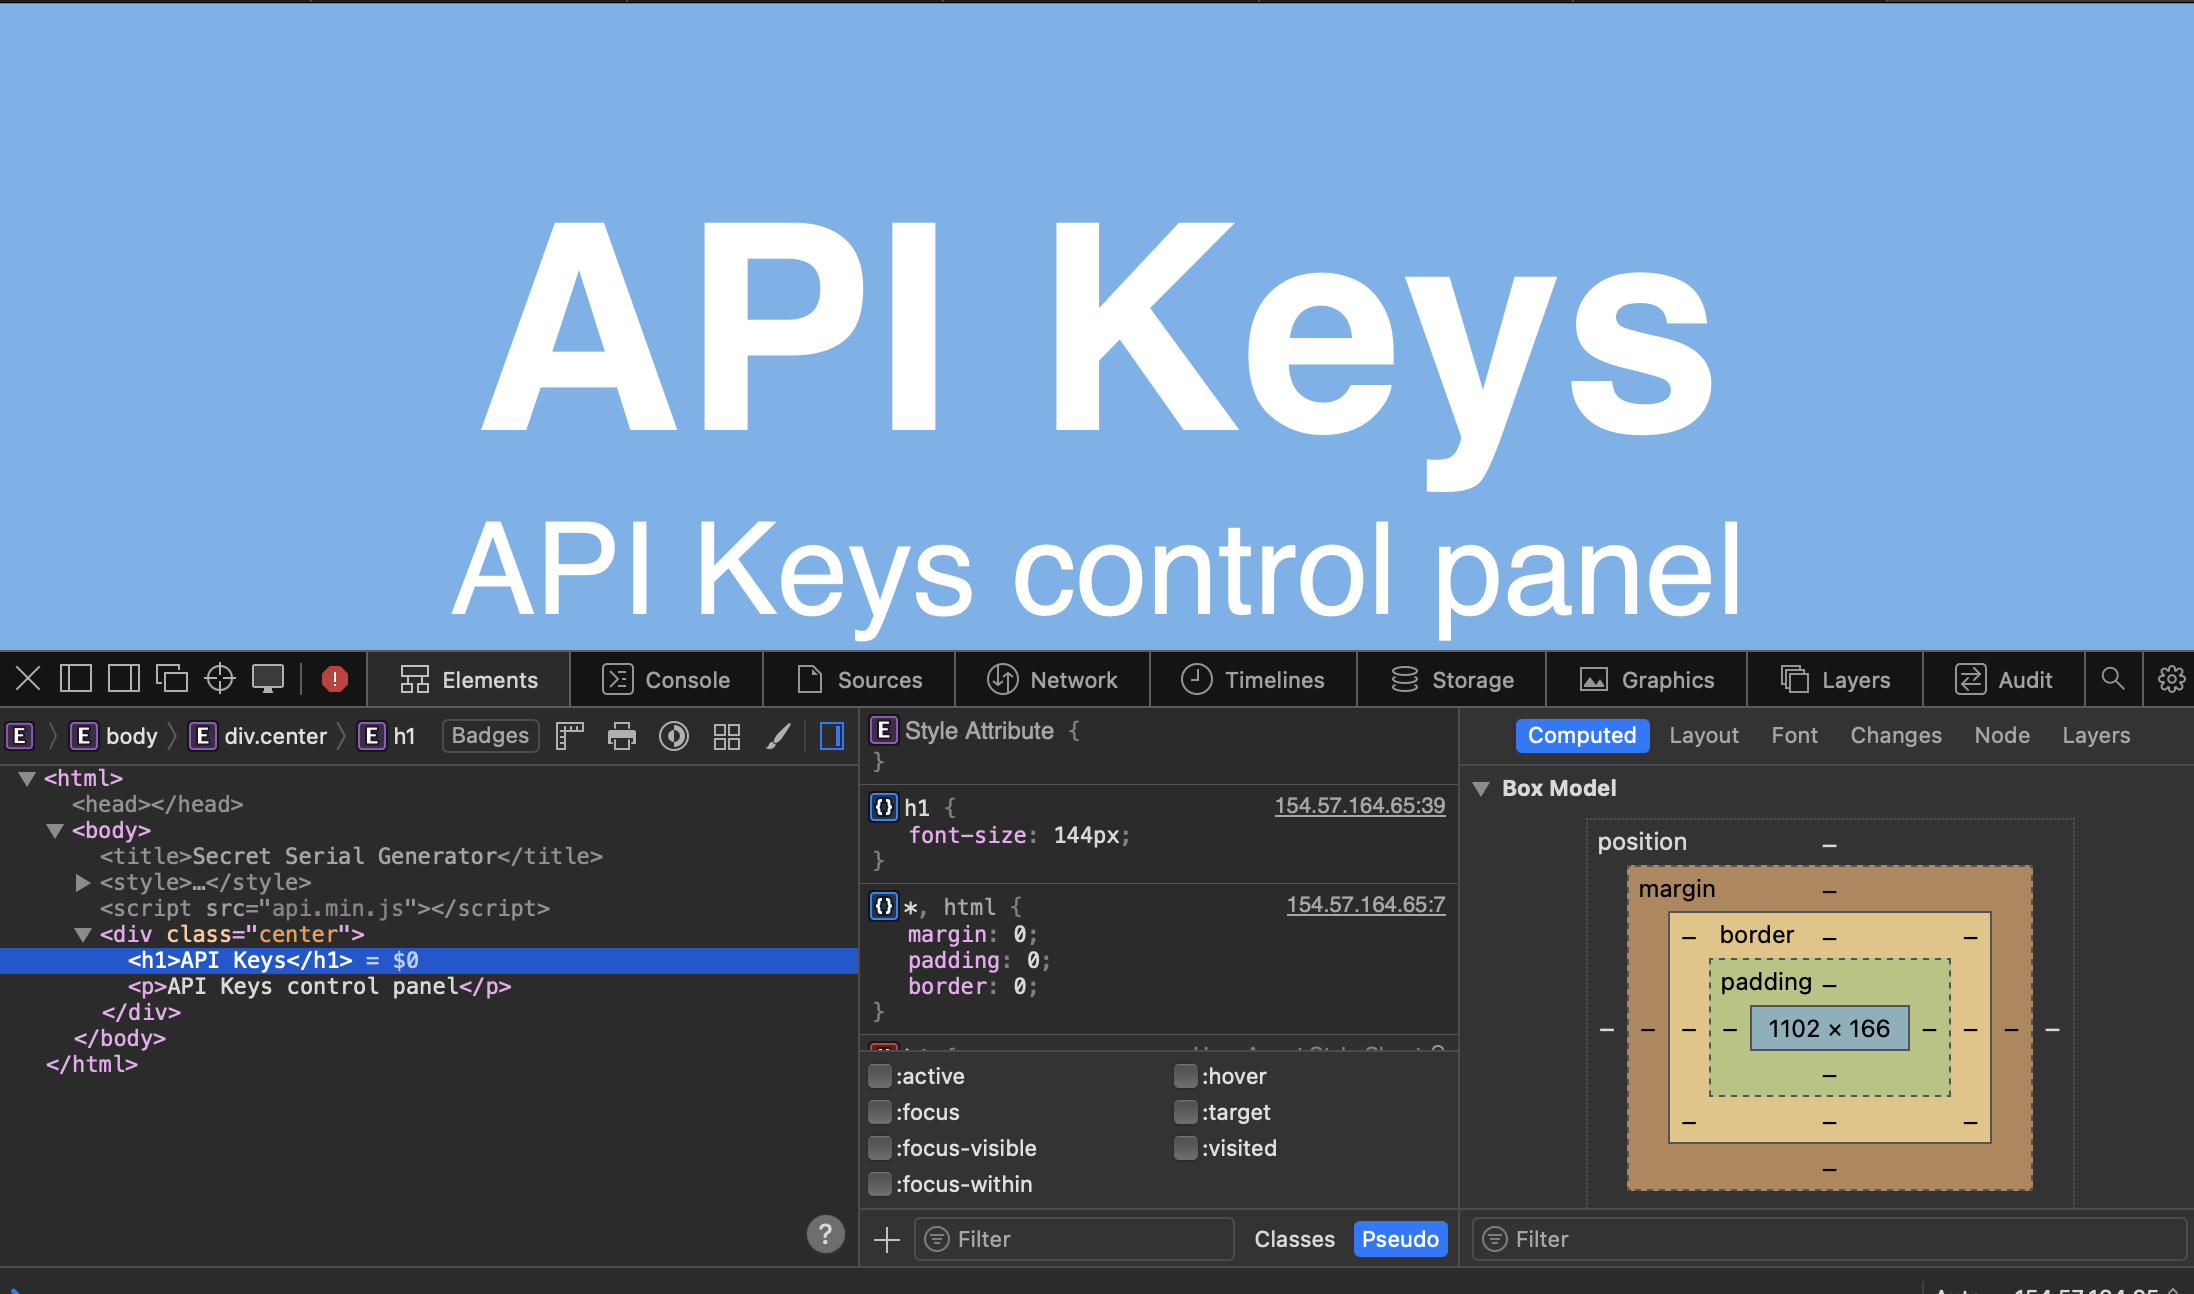
- Answer: api.min.js
Question 2: Once you find the JavaScript code, try to run it to see if it does any interesting functions. Did you get something in return?
- Let's click on the file to read it's content:
eval(function(p, a, c, k, e, d) {
    e = function(c) {
        return c.toString(36)
    };
    if (!''.replace(/^/, String)) {
        while (c--) {
            d[c.toString(a)] = k[c] || c.toString(a)
        }
        k = [function(e) {
            return d[e]
        }];
        e = function() {
            return '\\w+'
        };
        c = 1
    }
    ;
    while (c--) {
        if (k[c]) {
            p = p.replace(new RegExp('\\b' + e(c) + '\\b', 'g'), k[c])
        }
    }
    return p
}('t 5(){6 7=\'1{n\'+\'8\'+\'9\'+\'a\'+\'b\'+\'c!\'+\'}\',0=d e(),2=\'/4\'+\'.g\';0[\'f\'](\'i\',2,!![]),0[\'k\'](l)}m[\'o\'](\'1{j\'+\'p\'+\'q\'+\'r\'+\'s\'+\'h\'+\'3}\');', 30, 30, 'xhr|HTB|_0x437f8b|k3y|keys|apiKeys|var|flag|3v3r_|run_0|bfu5c|473d_|c0d3|new|XMLHttpRequest|open|php|n_15_|POST||send|null|console||log|4v45c|r1p7_|3num3|r4710|function'.split('|'), 0, {}))
- Let's copy it and run it in https://jsconsole.com
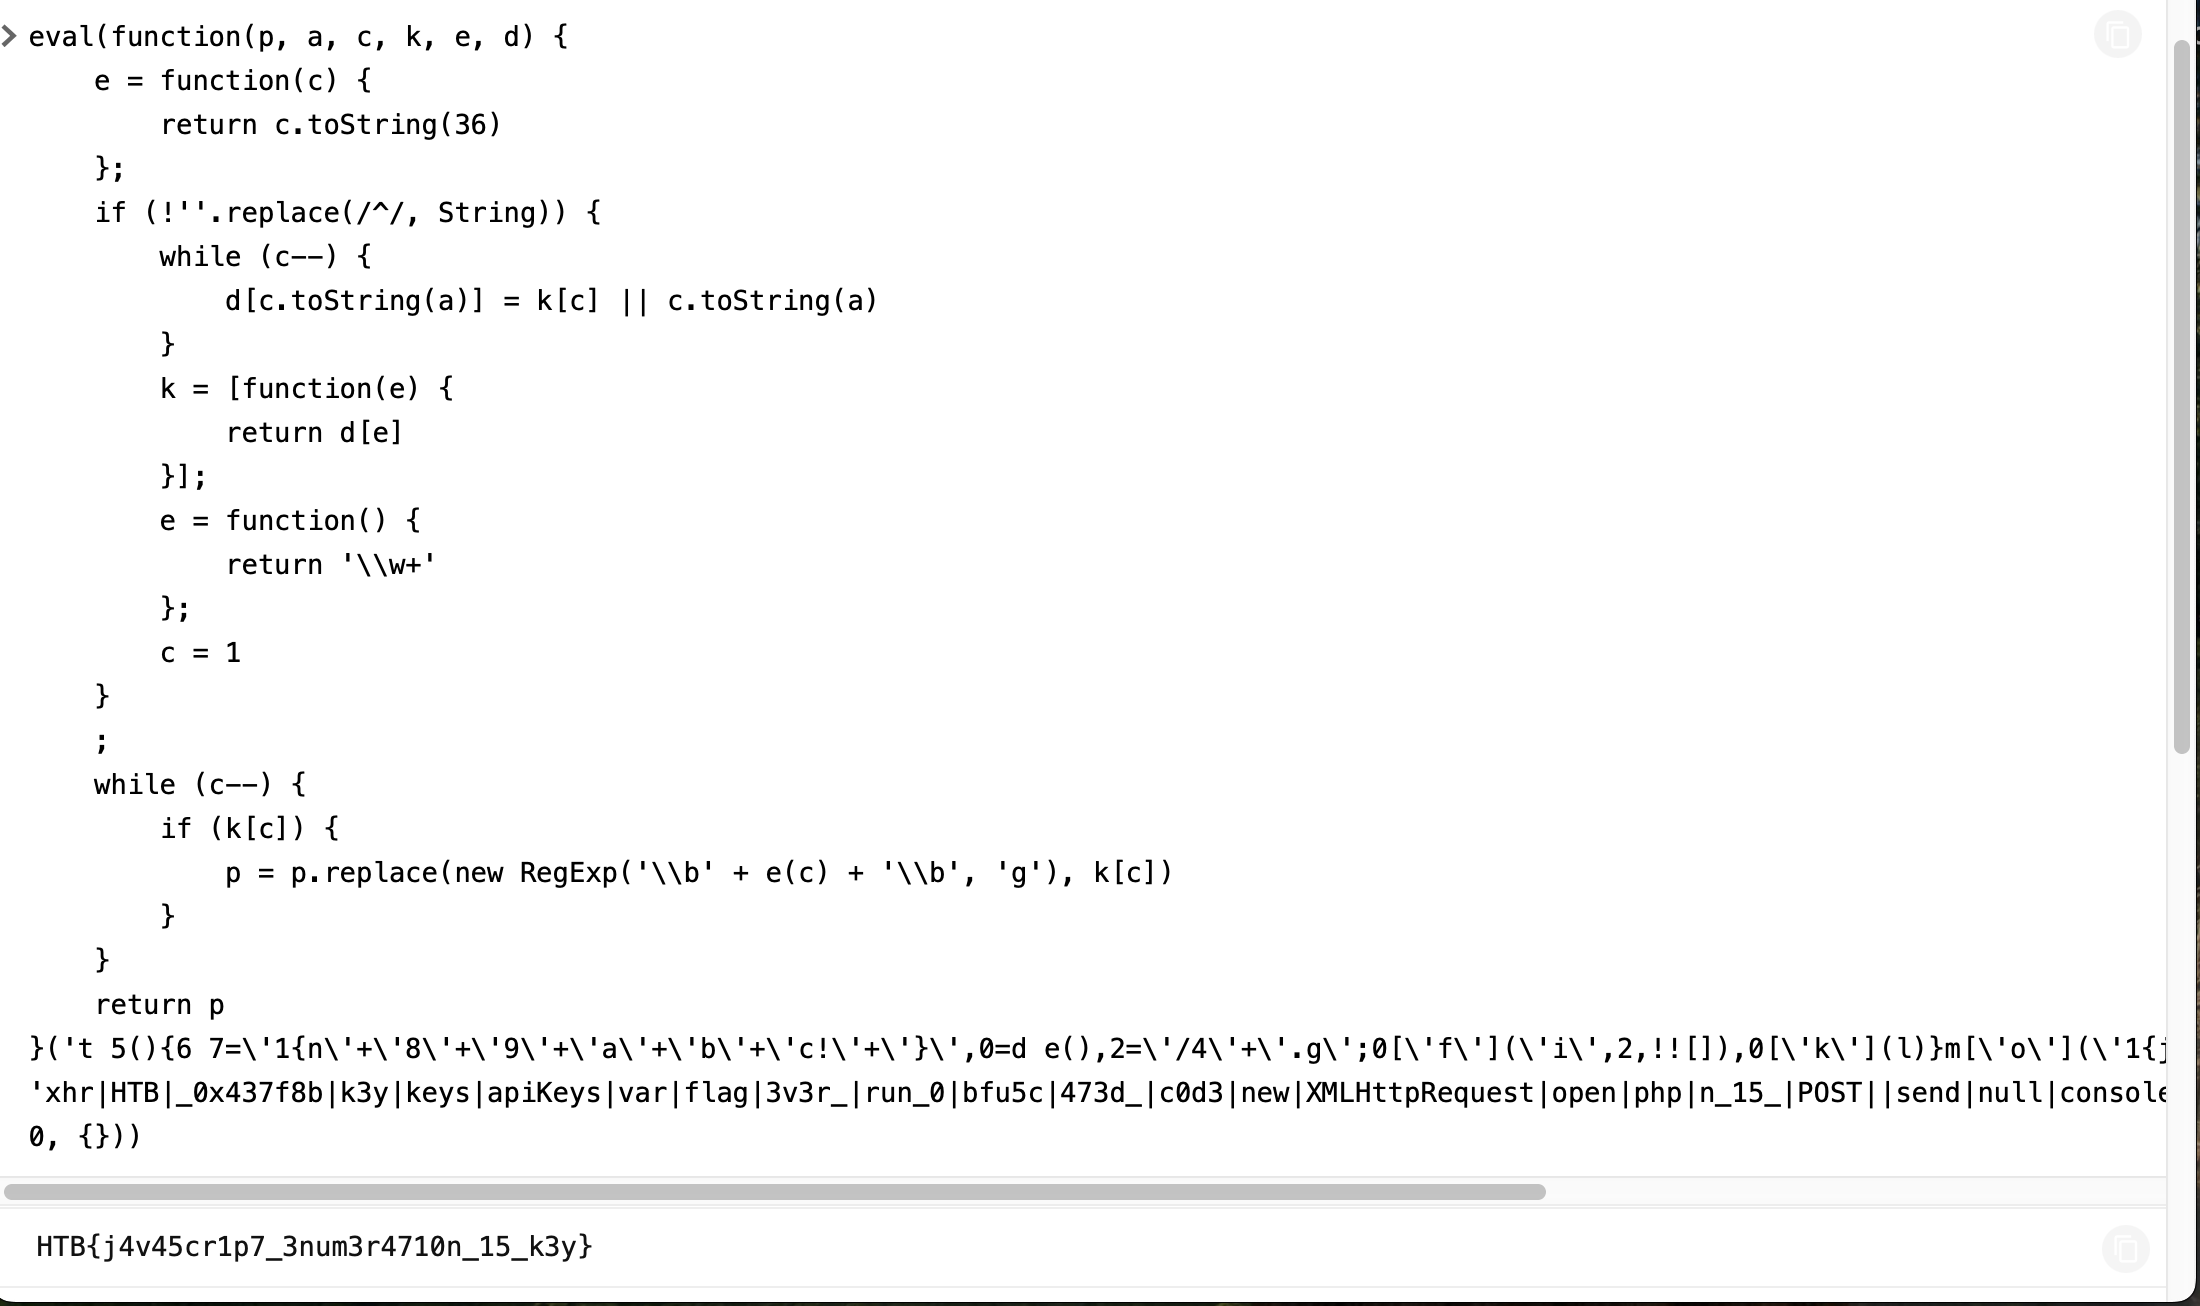
- Answer: HTB{j4v45cr1p7_3num3r4710n_15_k3y}
Question 3: As you may have noticed, the JavaScript code is obfuscated. Try applying the skills you learned in this module to deobfuscate the code, and retrieve the 'flag' variable.
- It seems the code inside
api.min.jsfile is obfuscated. Let's deobfuscate it using https://matthewfl.com/unPacker.html
#Deobfuscated result:
function apiKeys()
	{
	var flag='HTB
		{
		n'+'3v3r_'+'run_0'+'bfu5c'+'473d_'+'c0d3!'+'
	}
	',xhr=new XMLHttpRequest(),_0x437f8b='/keys'+'.php';
	xhr['open']('POST',_0x437f8b,!![]),xhr['send'](null)
}
console['log']('HTB
	{
	j'+'4v45c'+'r1p7_'+'3num3'+'r4710'+'n_15_'+'k3y
}
');
- Answer: HTB{n3v3r_run_0bfu5c473d_c0d3!}
Question 4: Try to Analyze the deobfuscated JavaScript code, and understand its main functionality. Once you do, try to replicate what it's doing to get a secret key. What is the key?
- It seems the javascript code is sending a POST request to
/keys.php
curl -s http://154.57.164.65:32543/keys.php -X POST

- Answer: 4150495f70336e5f37333537316e365f31355f66756e
Question 5: Once you have the secret key, try to decide it's encoding method, and decode it. Then send a 'POST' request to the same previous page with the decoded key as "key=DECODED_KEY". What is the flag you got?
- It seems the secret key is encoded with hex.
- Note: You can spot hex encoding by checking that a string uses only the characters
0-9anda-f/A-F, has an even total length (since each byte is represented by exactly 2 hex characters), and lacks symbols like=,+, or/that would instead point to something like Base64 — the string4150495f70336e5f...fits this pattern exactly, being 46 characters of strictly0-9/a-f, which is the classic tell for hex.
echo 4150495f70336e5f37333537316e365f31355f66756e | xxd -p -r

- Now, lets send a POST request with the decoded key as
"key=API_p3n_73571n6_15_fun"
curl -s http://154.57.164.65:32543/keys.php -X POST -d "key=API_p3n_73571n6_15_fun"

- Answer: HTB{r34dy_70_h4ck_my_w4y_1n_2_HTB}
Comments
Join the discussionNo comments yet. Be the first to comment.
HTB CWES Modules
Comprehensive HTB Certified Web Exploitation Specialist (CWES) Exam Prep — Full Module Walkthroughs Covering all official HTB Academy CWES modules with complete step-by-step walkthroughs, including interactive sessions and hands-on skill assessment solutions. Designed as a structured study guide to build both theoretical understanding and practical exploitation skills required for the CWES certification exam.